Results

News Analysis: IBM Watson Announces Data Driven Discovery Solution

News Analysis: IBM Watson Announces Data Driven Discovery Solution
New Discovery Advisor Solution To Help Researchers Answer The Tough Problems Never Answered Before

On August 28th, 2014 at the Museum of Art and Design in New York City, The IBM Watson group launched Discovery Advisor.  Mike Rhodin, SVP of IBM’s Watson Group, welcomed the audience to the Age of Discovery (see Figure 1).  In addition, Tom Malone,  Patrick J. McGovern Professor of Management at MIT discussed the new era of discovery with solutions such as Cognitive Computing.  Key announcements show how Discovery Advisor:

Figure 1. Mike Rhodin welcoming the crowd to the Age of Discovery

@mikerhodin #IBMWatson Age of Discovery Keynote

 Source: R Wang and Insider Associates, LLC All rights reserved.

  • Automates and augments human expertise. The discovery process comprises of four key areas: perceiving, reasoning, relating, and learning. IBM Watson stated goal is to “enable researchers to answer the tough research problems that have never been answered before”.  Watson Discovery Advisor understands natural language and reads/ingests journals, manuals, blogs, and social media to perceive.  Reasoning is achieved by making inferences, discovering relationships between concepts and definitions, determining pro’s and con’s, and providing context for complex problems. Watson relates concepts and personalizes interactions by tailoring responses, adapting and evolving, and delivering information in context with each interaction.  More importantly, Watson learns by training with human experts without any preset rules.  This self learning approach is the basis to the Watson Discovery Advisor (see Figure 2).

    Point of view (POV): In conversations with Soledad Cepeda, Director of Epidemiology at Janssen Research and Development, she explained how Discovery Advisor is ingesting research journals to automate and improve the research process to drive faster time to insight.  David Aldous, Head of Lead Generation to Candidate Realization at Sanofi described better return on R&D for therapies using the power of Watson to digest information internally and externally.  James Briscione, Director of Culinary Development at the Institute for Culinary Education discussed the recipe creation process and creation of new menus such as Austrian Chocolate Burritos.
  • Addresses discovery challenges across different industries.  Examples from industries included life sciences and research, engineering, public safety, and consumer.  City of Tuscon, Institute for Culinary Education, Institute for Electrical and Electronics Engineers, Janssen Research and Development, and The New York Genome Center showcased how Watson Discovery Advisor could be applied across a breadth of industry verticals.  Key challenges these industries over come include: 1) fragmented experiences where there are too many data sources to humanly review, and tools are limited to querying and reporting, 2) low probabilities of research success where data is siloed and stymied by processes, 3) lengthy and low return on investment projects that have high data crunching requirements and massive corporate compliance requirements.

    (POV): Two criteria emerge for common elements well suited for Discovery Advisor. First, professions that generate massive amounts of information beyond human capacity to consume and digest this information.  Second, professions that have a traditional apprentice approach to gaining expertise.  For life sciences and research, the rapid pace of information created has exceeded the human capacity to apply the latest collective intelligence.  David Goldstein, Lead Director for the Institute of Electrical and Electronics Engineers (IEEE), showed Watson could ingest tens of millions of patents and engineering documents and enable engineers to find answers in minutes versus months.  In law enforcement, Roberto Villasenor, Chief of Police in the City of Tuscon showed how the toughest crimes could be not only solved but also potentially prevented.  Consumer areas such as travel and food have been demonstrated at previous events.  However, the food prepared by IBM Watson Chef was definitely a great part of the experience in showing how new pallets and flavors can be created.


Figure 2. The Architecture Behind IBM Watson Discovery Advisor

@rwang0 @IBMWatson #DiscoveryAdvisor Archiecture

Source: IBM

The Bottom Line: The Age of Augmented Humanity Has Arrived

IBM Watson is basically augmenting humanity by converging of artificial intelligence, natural language processing, dynamic learning, and hypothesis generation to render vast quantities of data intelligible to help humans make better decisions. The ability to self-learn enables continuous reprogramming. These advancements represent a new class of technology to enable human and machine-guided decisions. Cognitive computing drives augmented humanity, where the sum of our collective insights and data can be served up at the right time in the right context. As IBM Watson continues to learn and grow, customers can expect new innovations to be suggested by IBM Watson (see Figure 3).  While this is hard to develop today, IBM Watson Discovery Advisor is as packaged as it gets in today’s market and customers looking to solve the tough innovation problems ahead should consider how this class of technologies can provide a unique competitive advantage.

Figure 3. The Progression of IBM Watson in The Age of Discovery

@rwang0 @ibmwatson the progression to cognitive

Source: IBM

Your POV.

Are you looking to reduce the time to market for discovery?  Do you see the possibilities of how a solution such as IBM Watson Discovery Advisor can transform your business?  Are you ready to test drive these solutions? Add your comments to the blog or reach me via email: R (at) ConstellationR (dot) com or R (at) SoftwareInsider (dot) com.

Please let us know if you need help with vendor selection efforts.  Here’s how we can assist:

  • Vendor selection
  • Implementation partner selection
  • Connecting with other pioneers
  • Sharing best practices
  • Designing a next gen apps strategy
  • Providing contract negotiations and software licensing support
  • Demystifying software licensing

Related Research:

Reprints

Reprints can be purchased through Constellation Research, Inc. To request official reprints in PDF format, please contact Sales .

Disclosure

Although we work closely with many mega software vendors, we want you to trust us. For the full disclosure policy, stay tuned for the full client list on the Constellation Research website.

* Not responsible for any factual errors or omissions.  However, happy to correct any errors upon email receipt.

Copyright © 2001 – 2014 R Wang and Insider Associates, LLC All rights reserved.
Contact the Sales team to purchase this report on a a la carte basis or join the Constellation Customer Experience!

The post News Analysis: IBM Watson Announces Data Driven Discovery Solution appeared first on A Software Insider's Point of View.


Data to Decisions Innovation & Product-led Growth Future of Work Tech Optimization Next-Generation Customer Experience Digital Safety, Privacy & Cybersecurity Event Report IBM ML Machine Learning LLMs Agentic AI Generative AI AI Analytics Automation business Marketing SaaS PaaS IaaS Digital Transformation Disruptive Technology Enterprise IT Enterprise Acceleration Enterprise Software Next Gen Apps IoT Blockchain CRM ERP finance Healthcare Customer Service Content Management Collaboration Executive Events Robotics Cloud Quantum Computing CCaaS UCaaS Enterprise Service developer Metaverse VR Supply Chain Leadership Chief Customer Officer Chief Information Officer Chief Executive Officer Chief Technology Officer Chief AI Officer Chief Data Officer Chief Analytics Officer Chief Information Security Officer Chief Product Officer Chief Experience Officer

Twitter Kills More of Its Darlings-Tweet Analytics for All

Twitter Kills More of Its Darlings-Tweet Analytics for All

1

In writing, you must kill your darlings.
– William Faulkner

Ever since my first reading, I have loved William Faulkner. His genius leapt through the page to punch the reader in the throat. And while this quote about murdering your darlings – your favourites, your supporters, your most dearly treasured – can truly be attributed to him is doubtful. But when it comes to creativity, there is a certain dramatic logic to it. After all, it’s easy to learn to love something that you have struggled to bring to life. And for the reader, that struggle – in the reading – is also acknowledged. We read in struggle or defiance as much as we read in love. So when an author kills her darlings, the characters, situations etc that she created, the reader also shares in the loss. The drama. The agony. And the surprise.

And this is the great reward.

But when I see this approach applied to businesses – especially to startups – I baulk. In this always-connected world, it’s a struggle to create something new, useful and easy to adopt (unless it’s a puppy). It is hard to “cut through”. Hard to build an audience and generate traction with a cynical community. And it is hard to attract customers, scale through your technical challenge, attract funding and talent, and build a culture that empowers employees, attracts customers and satisfies stakeholders.

In short, the challenge is in creating a participatory ecosystem with enough value to go around.

TwitterAnalytics

With this in mind, I greet the release of Twitter Analytics with a smile AND a shrug.It is great for Twitter users who have an interest in data, impact and so on, but it is yet another anti-ecosystem move. It’s like LinkedIn’s recent decision to close off API access to sites such as Nimble. On the one hand it makes sense. “Consolidate. Be all things to all people. Own the platform.” But on the other hand, it’s limited and limiting. It’s an attempt at monetising without an ecosystem vision. And it is an affront to the users who have invested not just in the platform (Twitter, LinkedIn and yes Facebook too), but in the ecosystem as well.

In some cases our investment has been made in dollars, but that usually pales into insignificance when we evaluate our time, effort and process commitments.

Now, there is no doubt that Twitter Analytics will be useful because it provides people like myself with access to powerful data analysis tools. I dare say, eventually, it will evolve into a suite of tools that I can pay for too (more ways to monetise).

But the release of Twitter Analytics will stop external growth and investment in the Twitter ecosystem. It means that the plethora of businesses (large and small) that have sprung up thanks to the goldmine of real-time data available through social networks such as Twitter, Facebook and yes, even Google+ have one less reason to be. And thousands of less customers to attract. On that list will be everyone from Tweetreach to Hootsuite.

But the bigger challenge that comes with killing your darlings, is that they are not yours alone. And when you turn on something your customers love, you lose a little bit of that love that we had for you. And eventually, as with all disruptions, there will come a time when something or someone newer and shinier will come along. That’s when you – Twitter – will want every ounce of loyalty to play out. But by then you’ll have squandered it.

If I have learned anything from the world of software, it is that ECOSYSTEMS WIN in the long run. And if you really do want to change the world and be part of every person’s digital life, the likes of Twitter and LinkedIn would do well to think big – not just for themselves, but for all their stakeholders. Kill your darlings by all means, just make sure your aim is true.

Marketing Transformation Next-Generation Customer Experience Revenue & Growth Effectiveness X Chief Customer Officer Chief Marketing Officer Chief People Officer Chief Revenue Officer

Infosec Doesn’t have to be a Four Letter Word

Infosec Doesn’t have to be a Four Letter Word

1

I wrote earlier this week about Identity and Access Management (IAM) and how it’s important for Infosec (Information Security) to be involved with projects early. The post generated a few comments and some commentary on twitter, mostly from Infosec folks. Some complained I was too harsh on Infosec (I wasn’t) while others worried that I didn’t go into enough depth (I didn’t). In my mind though, it raised the issue of why there is such friction between Infosec folks and the rest of IT.

infosecLet me start by saying security is hard. That’s just a fact of life. It’s difficult to secure against everything, especially when many of those things are unknown. Yet, it doesn’t mean we should forget about security, but we do have to be realistic. If someone really wants to cause you a problem and is determined enough to, they most likely will succeed. Your job is to make it a little harder for them and to prevent as much damage as possible. At the same time, your goal is to make sure that the doors aren’t left wide open for those who are passing by and could see an opportunity.

Don’t forget my disclaimer, I am not an Infosec guy and I don’t even play one on TV. That being said, I believe that security in an organization is everyone’s responsibility. It’s not just all those hard working people in Infosec, they lead the charge but they still need the army to back them up. We, the every day employees are that army. We have to understand the basics, things like having a good password, not leaving your device open and logged in while at the coffee shop, and understanding what a phishing email looks like among others. When we see something funky going on, we should say something.

This is where some of that friction comes in. Not everyone in Infosec believes that every person should be doing security. They believe it’s their job only. My answer, grow up; you have better things to worry about. When you partner with your users you will have a much easier time getting stuff done.

The second place that friction comes in is simple; many in Infosec think that every day users are stupid. They need to be protected from themselves and Infosec is more than happy to oblige. Among other things, they throw up proxy servers that cut off all contact with the outside or they setup firewall rules that block everything. Infosec then wonders why everyone is going outside of the work network to get things done. They use their phones as wireless hotspots, they figure out a backdoor to getting around the proxy server, or if they’re really smart, they discover that a VPN defeats all that magic blocking. A lot of this is done to manage risks without understanding rewards. Years ago, I was in a new job and one of the things I had to research was Mobile IM clients. Nothing fancy but a way to connect our internal IM with our mobile devices on the go. I fired up my browser and quickly discovered that all ‘chat’ client websites were blocked. Ok, fair, I went and got a security dispensation, as it was my job requirement to understand these products after all. It took, after getting an approved dispensation, arguing with 2 different security personnel and then 4 weeks working with the firewall person to create the exception to the rule. Do you think I stopped working on the task at hand during those 4 weeks, absolutely not. I found a way around the issue and got my work done. It was my own little case of shadow innovation.

One of the things that Infosec really has to do is learn to work with their users. It’s much easier to have people follow the rules when the rules make sense to both sides. That doesn’t mean you have to let people run wild. Just that you have to work with them and understand there needs. Infosec is as much about security as it is risk management. One of the best ways to manage risk is to work with people and figure out the best way to enable them in a secure way. It’s time for Infosec to move away from the department of No and become the department of Know, where it’s about securely enabling people. This is going to require Infosec to become design thinkers. They will need to understand how to make security work in systems that are being modified every 6-12 weeks so people can be more productive.

It also requires that the business, IT, and the developers start trusting Infosec. They can’t stick with the same model of designing an app or project, building it, and when release time rolls around submitting it to security for approval. That’s a direct line to a deserved delay or freeze in a project. The Infosec team has to be involved in projects from day one. If they are expected to be design thinkers, they need to be involved with the actual design of the product. Only when they are aware of the business requirements and understand the users’ needs can they truly enable the product securely.

In the end, the goal of Infosec has to be to minimize the risks a company is facing while at the same time enabling their users. It’s not an either/or proposition. If you do one without the other, you will eventually fail.

Related: 

FIDO Alliance Update: IDAM Implications for a World of Digital Business by Steve Wilson

New C-Suite Digital Safety, Privacy & Cybersecurity Tech Optimization Future of Work Infosec Security Zero Trust Chief Information Officer Chief Information Security Officer Chief Privacy Officer

Walked 6 Miles First Day of Electric Car

Walked 6 Miles First Day of Electric Car

1

My walking was not the fault of the car; the car is great. The car is, however, part of a bleeding-edge ecosystem of apps, charging stations, employer support for sustainability, parking rules, university websites, and my commuting choices. I thought I had followed my own advice to work with all my human, organizational, and technological resources -- but it just wasn’t so.

What I Did to Prepare

  • Verified that I can get to work (47 miles) on a single charge (85 miles, 104 with special option)

  • Verified on website that my employer offers free charging with valid ($300/year) parking permit

  • Pre-registered with the charging network installed in the parking lots

  • Studied map of chargers across the different parking lots at work -- those near my office are free!

  • Bought car, downloaded apps to track charging, registered the keytag sent by charging network

What Happened

  • Drove to work and parked at free charger -- “Not Authorized” blinks after using my pre-registered tag

  • Called the charging network help number, told I need a number provided by my employer

  • Deep dive into employer’s website (using smartphone from parking lot) -- including filling out newly discovered online form to get needed secret code

  • Ate lunch while waiting on secret code

  • Walked to my organization’s parking office to learn more face-to-face and ask if code could be expedited

  • Moved car to other side of campus pay-as-you-go charger while waiting for code 

  • Got some work done (sidenote: someone unplugged car before it was fully charged -- not cool and against the etiquette of charging station use -- app messaged me, but didn’t take a picture of the perpetrator, would be useful feature)

  • Received secret code and submitted it to charging network website, saw that approval status switched to pending

  • Moved car back to free charger after receiving email of approval

  • “Not Authorized” still blinking

  • Called charging network help number and then moved car back to distant pay-as-you-go charger when told approval hadn’t percolated through all the databases to the charger and it could take overnight

  • Skipped going to the gym (I’d done some par course pull ups on one of my six walks across campus)

  • Got some work done

  • Drove home -- 16 "miles" left as it didn't have time for a full charge

What I Should Have Done

  • Realized it couldn’t be as easy as just pulling up to the charger I’ve been driving by for six months. It never is. That would be a silver/magic bullet and those don’t exist -- unicorns maybe; magic bullets, no way. No single technology, person, or organizational system stands alone.

  • Realized that electric car ecosystems are new for everyone and that the people in the parking office will have the curse of knowledge  -- they know how the system works, so communicating the practices to novices is more difficult, especially if they haven’t had to go through it themselves.

  • Gone deeper than the promotional material on my employer’s website. Yes there is free charging, but you have to be pre-approved by both the employer and the charging station network -- takes time and several loops of interaction as there is money at stake. Don’t expect the Internet of Things to come together in one day.

  • Taken note of who’s describing the process that seems so simple. The version that made it appear seamless was coming from our sustainability office, not the people who run parking and have to do the verification. The sustainability office must manage their search engine optimization better as theirs was the top result.

Systems like this are our reality and our future. As I look at my desk, I think my coffee cup is the only thing that isn’t part of a larger system of interactions. My Hint water has codes in the cap I use for promotions. My TV remote is just the beginning of three levels of service providers. Every piece of paper is tied to a website and system of deeper interactions.

What I Learned

If it looks easier than you expect, dig deeper. Think about each of the interactions across the human, technical, and organizational dimensions and what has to be happening in the background. Had I gone through a full checklist, it would have occurred to me that there had to be a way to tell the charger that I had the right to free power -- there had to be a secret code/handshake/incantation and I should have been looking for it. Then again, I did walk off my lunch.
New C-Suite Chief Customer Officer

Engaging engineers in privacy

Engaging engineers in privacy

Updated from original post January 2013.

I have come to believe that a systemic conceptual shortfall affects typical technologists' thinking about privacy. It may be that engineers tend to take literally the well-meaning slogan that "privacy is not a technology issue". And I say this in all seriousness.

Online, we're talking about data privacy, or data protection, but systems designers bring to work a spectrum of personal outlooks about privacy in the human sphere. Yet what matters is the precise wording of data privacy law, like Australia's Privacy Act. To illustrate the difference, here's the sort of experience I've had time and time again.
During the course of conducting a PIA in 2011, I spent time with the development team working on a new government database. These were good, senior people, with sophisticated understanding of information architecture, and they'd received in-house privacy training.
But they harboured restrictive views about privacy. An important clue was the way they habitually referred to "private" information rather than Personal Information (or equivalently, Personally Identifiable Information, PII). After explaining that Personal Information is the operable term in Australian legislation, and reviewing its http://lockstep.com.au/blog/2013/09/27/pii-or-not-pii">definition as essentially any information about an identifiable person, we found that the team had not appreciated the extent of the PII in their system. They had overlooked that most of their audit logs collect PII, albeit indirectly and automatically, and that information about clients in their register provided by third parties was also PII (despite it being intuitively 'less private' by virtue of originating from others).

I attributed these blind spots to the developers' loose framing of "private" information. Online and in privacy law alike, things are very crisp. The definition of PII as any data relating to an individual whose identity is readily apparent sets a low bar, embracing a great many data classes and, by extension, informatics processes, but it's a nice analytical definition that is readily factored into systems analysis. After getting that, the team engaged in the PIA with fresh energy, and we found and rectified several privacy risks that had gone unnoticed.

Here are some more of the recurring misconceptions I've noticed over the past decade:

  • "Personal" Information is sometimes taken to mean especially delicate information such as payment card details, rather than any information pertaining to an identifiable individual; see also this exchange with US data breach analyst Jake Kouns over the Epsilon incident in 2011 in which tens of millions of user addresses were taken from a bulk email house;
  • the act of collecting PII is sometimes regarded only in relation to direct collection from the individual concerned; technologists can overlook that PII provided by a third party to a data custodian is nevertheless being collected by the custodian; likewise technologists may not appreciate that generating PII internally, through event logging for instance, also represent collection.

These instances and others show that many ICT practitioners suffer important gaps in their understanding. Security professionals in particular may be forgiven for thinking that most legislated Privacy Principles are legal technicalities irrelevant to them, for generally only one of the principles in any given set is overtly about security; see:

  • no. 5 of the OECD Privacy Principles
  • no. 4 of the Fair Information Practice Principles in the US
  • no. 8 of the Generally Accepted Privacy Principles of the US and Canadian accounting bodies,
  • no. 4 of the older National Privacy Principles of Australia, and
  • no. 11 of the new Australian National Privacy Principles.

Yet all of the privacy principles in these regimes are impacted by information technology and security practices; see Mapping Privacy requirements onto the IT function, Privacy Law & Policy Reporter, Vol. 10.1& 10.2, 2003. I believe the gaps in the privacy knowledge of ICT practitioners are not random but are systemic, probably resulting from privacy training for non-privacy professionals not being properly integrated with their particular world views.

To properly deal with data privacy, ICT practitioners need to have privacy framed in a way that leads to objective design requirements. Luckily there already exist several unifying frameworks for systematising the work of development teams. One tool that resonates strongly with data privacy practice is the Threat & Risk Assessment (TRA).

A TRA is for analysing infosec requirements and is widely practiced in the public and private sectors in Australia. There are a number of standards that guide the conduct of TRAs, such as ISO 31000. A TRA is used to systematically catalogue all foreseeable adverse events that threaten an organisation's information assets, identify candidate security controls to mitigate those threats, and prioritise the deployment of controls to bring all risks down to an acceptable level. The TRA process delivers real world management decisions, understanding that non zero risks are ever present, and that no organisation has an unlimited security budget.

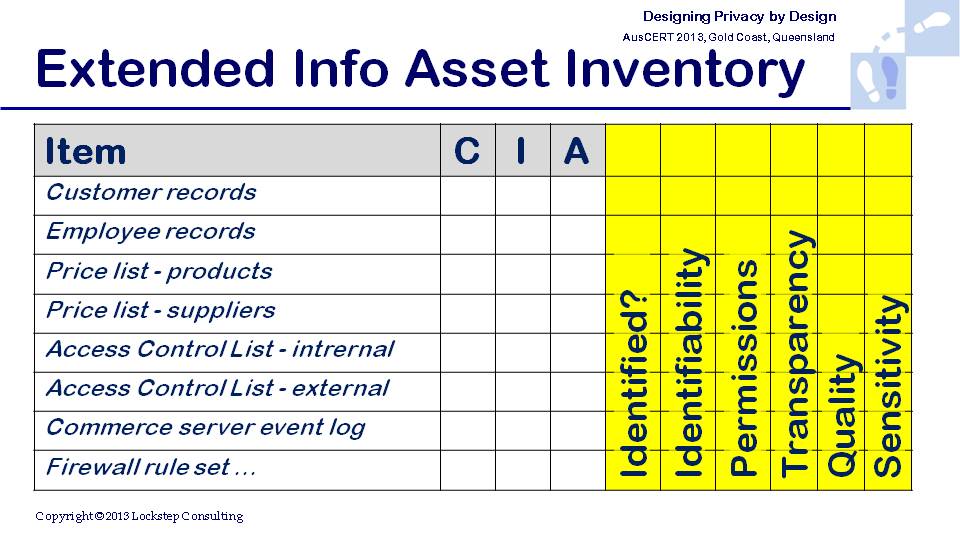
The TRA exercise is readily extensible to help Privacy by Design. A TRA can expressly incorporate privacy as an aspect of information assets worth protecting, alongside the conventional security qualities of confidentiality, integrity and availability ("C.I.A.").

A crucial subtlety here is that privacy is not the same as confidentiality, yet they are frequently conflated. A fuller understanding of privacy leads designers to consider the Collection, Use, Disclosure and Access & Correction principles, over and above confidentiality when they analyse information assets. The table below illustrates how privacy related factors can be accounted for alongside "C.I.A.". In another blog post I discuss the selection of controls to mitigate privacy threats, within a unified TRA framework.

We continue to actively research the closer integration of security and privacy practices.

Data to Decisions Future of Work New C-Suite Next-Generation Customer Experience Digital Safety, Privacy & Cybersecurity Security Zero Trust Chief People Officer Chief Information Officer Chief Information Security Officer Chief Privacy Officer

Why Do People Leave Jobs?

Why Do People Leave Jobs?

1

When I begin working with clients I work to understand what their ambassadors think about them. I look to their customers and suppliers to get a sense of what is working and what is not. But there is no better source of insight than a company’s employees. These are the people who are actively engaging and promoting the company every day. They are the face of the brand and are – in many instances – the custodian of customer experience. If an employee is having a bad day, your brand is likely to feel the impact.

This infographic from Bamboo HR is based on interviews with over 1000 US-based employees. And they look not just at the reasons that people leave, but the conditions that make people unhappy. Because unhappy employees perform worse than happy ones. No surprises there, right? But there is a substantial difference between an employee who is unhappy and a company culture that MAKES people unhappy. And far too often, the reasons that people are unhappy is not to do with the people that they work with, but the conditions that they work under.

Take a look at the statistics in this infographic. Do these situations worry you? Do some of these apply to your business? Do you even know?

There are ways to fix this and it may be easier than you imagine. Let’s chat!

Workplace-Deal-Breakers-Infographic

Future of Work Next-Generation Customer Experience Marketing Transformation Innovation & Product-led Growth Tech Optimization Chief Customer Officer Chief People Officer

Facebook to Fix Security Issue in iOS App

Facebook to Fix Security Issue in iOS App

1

So, the downloading and use of a Facebook App could create security threats? Who'd have thunk it? Oh, wait...I could, and did right here on Huffington Post.

Last December I posted an article calling out the Android permission settings on the Facebook Messenger app and others like it. I highlighted the threat that the "without your permission" stipulation, among others, could open the door for malicious third party software or hackers to gain access to your smart phone.

The article created quite a stir when it went viral last month when Facebook began removing the IM function from within its social networking app. For the most part, readers shared my concern; however, a select group of self-proclaimed tech geeks suggested that I was misinforming people and that I was just paranoid. Others pointed to the fact that the permission settings were specific to Android and that the sandboxing offered on Apple's iOS would prevent such unauthorized access from occurring.

Was I really paranoid? Are security issues only possible on Android apps thanks to the manner in which it manages permission settings? Well, earlier this week Andrei Neculaesei, a developer at Copenhagen-based Airtame, discovered a dangerous bug in the Facebook iOS app's programming that might cause potentially expensive calls to be made with your iPhone, without requesting your permission.

Neculaesei shares how the bug works on his blog where he explains that there's a potential for your iPhone's calling function to be hijacked when you click on a web link. He calls the bug "some sneaky-beaky-like JavaScript," which makes the links embedded in websites click themselves.

The threat could be even bigger. Neculaesei predicts that the vulnerability in theses apps could automatically transmit a video feed to attackers when clicking on a link within Facetime, for example. Facebook has announced that it has already developed an update to address the security threat; however, a release date has yet to be listed as of the date of this post.

Are We Right to be Paranoid?

My security concerns over our increasing use of mobile apps, for which we rarely read the permission settings or terms of service, were met with harsh criticism by some who said I was wearing a tinfoil hat and breeding paranoia.

I hate to say "I told you so" but, well, there it is. One of the potential threats I feared has come to life.

Will there be others? Of course there will.

Should you delete all your mobile apps? Of course not.

What we should do is start taking the time to read the fine print before we download apps that request access to our phone's data and functionality, and really consider if the app's utility is worth the potential security risks that may come with using it.

Next, we must put more pressure on app manufacturers to be clearer and more specific about how and why they need to access certain data and functions on our phones, and offer limitations on how that data will used once collected.

Finally, we must start to insist that they add greater safeguards to protect our data or we'll stop downloading them.

What say you? Are you at all concerned about the increased threat posed by the permission settings and/or terms of use we accept when downloading modern apps?

New C-Suite Next-Generation Customer Experience Marketing Transformation Digital Safety, Privacy & Cybersecurity Infosec meta Marketing B2B B2C CX Customer Experience EX Employee Experience AI ML Generative AI Analytics Automation Cloud Digital Transformation Disruptive Technology Growth eCommerce Enterprise Software Next Gen Apps Social Customer Service Content Management Collaboration Security Zero Trust Chief Customer Officer Chief Information Officer Chief Information Security Officer Chief Privacy Officer

Event Report - VMware makes a lot of progress - but the holy grail is still missing

Event Report - VMware makes a lot of progress - but the holy grail is still missing

I had the chance to attend VMworld in San Francisco this week, blogged my Day 1 takeaways here, time to blog on the overall impressions of the event. 

Here are my Top 3 takeaways:
  • End User Computing (EUC) is getting bigger and bigger for VMware - It’s only 12 months ago when the industry pundits gave VMware (rightfully) a hard time on the direction of EUC, especially around the future of SocialCast. Well – what a difference a year makes: The VMware EUC portfolio is growing fast and partnering left and right in the industry (e.g. partnerships with heavyweights like Google, NVidia and SAP were announced on stage today). And the EUC story ties nicely into the overall story of VMware using vCloud Air – probably the EUC products are the largest load that VMware can drive into the data centers that run vCloud Air. The hospital doctor demo that Poonen and Colbert showed on stage showed some key progress on how people should work – transferring sensitive data (patient X-Ray images) safely between heterogeneous devices with the help of Airwatch content locker. But is should be even easier – and it’s good to hear that VMware is working on usability and some next generation capabilities. And the provisioning of applications with CloudVolumes demos looks like … black magic. It’s good to see that VMware is ruthlessly working on reducing the cost of running a desktop as lower costs make more usage scenarios available and lower cost helps the overall adoption of virtual desktops. 

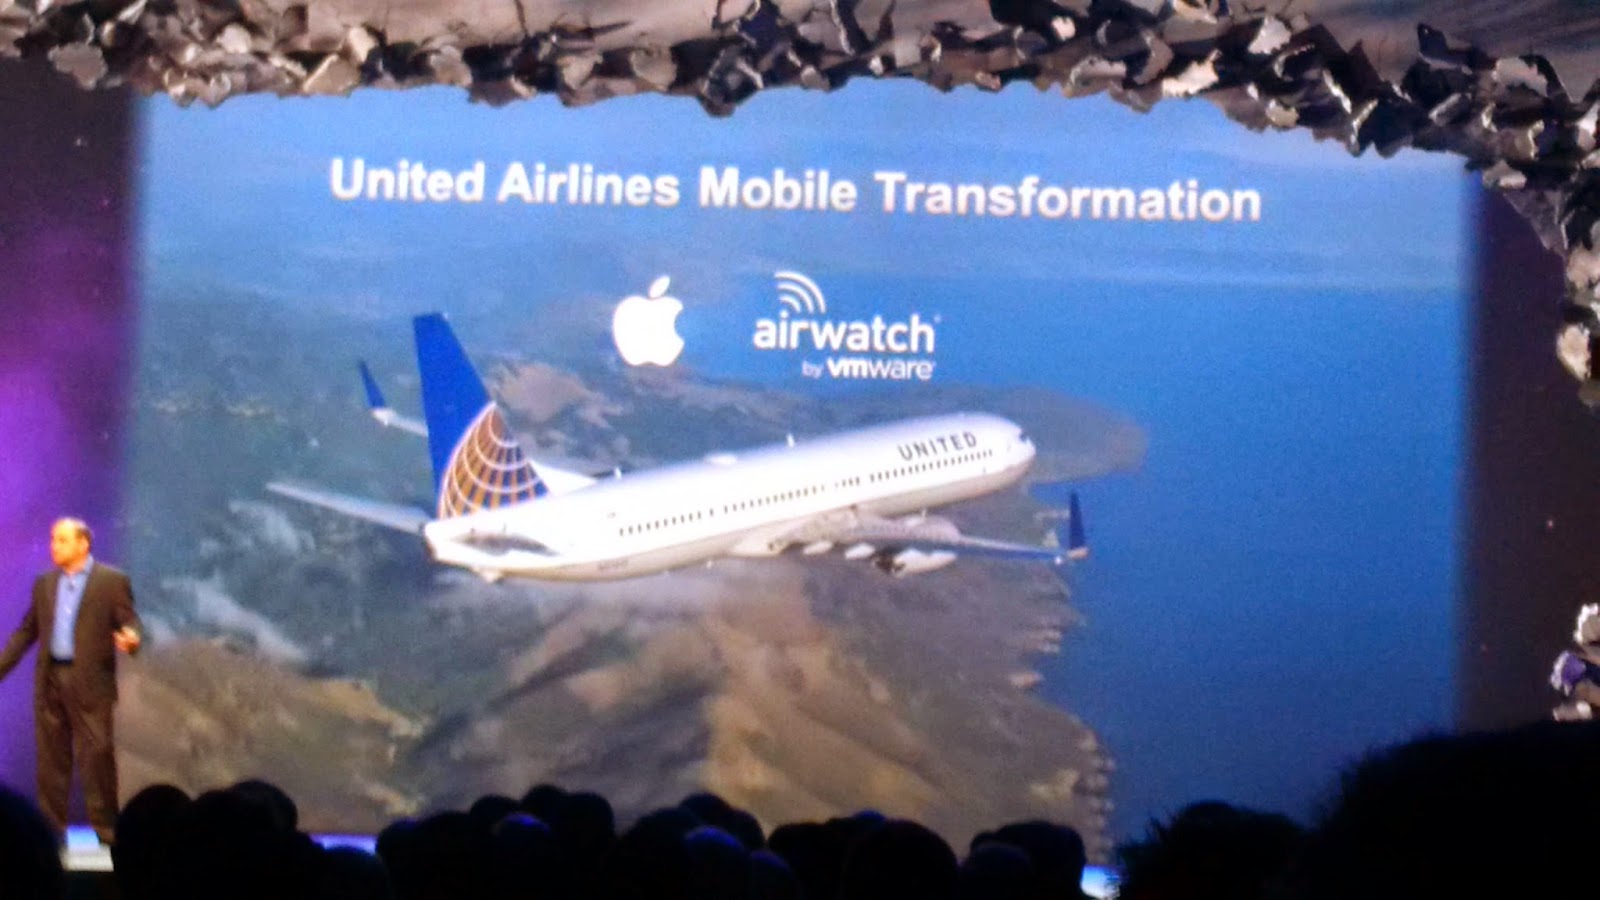
Poonen talking about United's iPads for Pilots, poweredd by Airwatch

  •  OpenStack & Containers - revisited - The OpenStack and various container partnerships received more attention today – and combined with the afternoon briefings of yesterday the picture here gets much clearer on the business side. Kudos to VMware executives to share that customer demand is one (or the key) driver here. And while the OpenStack move is more defensive – yes customers can run now from an OpenStack console a VMware powered data center under hoods – the container move is critical as it gives VMware some chops into the important next generation applications business. Enterprises build these next generation applications primarily on the public cloud, using the popular containers. For VMware to bring back that load to the corporate data center is a key move to extend the life of a VMware powered data center. They key factor here will be TCO – on both cases – OpenStack and containers – and comes back to VMware being able to reduce the cost to run VMware powered data centers. VMworld showed that VMware looks at cost, e.g. in the EUC space – but in general my impressions were, that VMware is trying to add value with NSX and more to keep the license share / revenue constant. A valid strategy but it may be challenged with the zero to very low license costs seen with OpenStack and Open Source in general. 

OpenStack and VMware [Pardon bad picture quality]

  • Hybrid Cloud - gaining traction - Good to see VMware moving ahead in this key area – but at less speed than I am afraid is important for the company and its customers. Brunozzi demoed a nifty DR scenario – where vCloud Air is being used for disaster recovery. But VMware can and needs to do so much more here. Granted it’s early days but the dynamic shifting of loads is the business case that is really what VMware needs to address – better sooner than later. If VMware is early in addressing this – they can be part of the shift of a more growing part of enterprise automation being powered by the public cloud providers. One of the most welcomed demo features was the vMotion of a VM over long distance. So with VMware using the same platform both on the on premise and cloud side, the capability is there. But the longer VMware will not address this – the more customers will vote with their feet – or more with a lot of work and investment for other vendors – moving loads to the public cloud. 

The 4 vCloud Air services - for now.

MyPOV

A lot of progress by VMware at this VMworld. Granted all announcements are still out and a ot of product has to be build – some of these products being almost a year out. It is good to see VMware listening to customers, but the very reason customers are asking for support for e.g. OpenStack and containers is that the want to have less lock-in – and the largest virtualization lock-in market share wise is with VMware. It comes back to VMware to create constantly more value around that – after all who wants to leave a golden cage? 

But at the same time the warning bells should be ringing in the executive team around Gelsinger. For the longest time I was thinking that VMware was a hostage of the high margins it monetizes from its on premise business. In conversation with executives I was convinced though that – if done right – VMware could generate even more revenue if moving these customers to the public / VMware cloud. So the question is what is holding VMware back? It is certainly not the CAPEX challenge many of its partner faces, both VMware and EMC have deep enough pockets. I am convinced it is also not the executive team not ‘getting this’. So what remains is a product roadmap challenge – VMware needs to build product to attract customers to build next generation applications on the VMware cloud and find a solution to move on premise load dynamically to the public cloud. Which will be a hybrid cloud scenarios – and I remain with my verdict that this remains the Holy Grail for VMware – as no vendor knows and understands current enterprise workload as well as VMware. VMware did not announce any capabilities here – maybe it will surprise us in the next quarters to come. 

In the meantime the EUC portfolio is making great progress – if the team around Poonen can keep the momentum 2015 will be an even more exciting year for the VMware EUC portfolio.


More on VMWare by me

  • First Take - VMware's VMworld Day 1 Keynote - Top 3 Takeaways - read here.

  • Progress Report - Good start for VMware EUC - time for 2nd inning - read here.

  • Speed Briefings at VMworld - inside and outside the VMware ecosystem - read here.

  • VMware defies conventional destiny - SDDC to the rescue - read here.


Tech Optimization Innovation & Product-led Growth Data to Decisions Digital Safety, Privacy & Cybersecurity Future of Work vmware Google Microsoft SaaS PaaS IaaS Cloud Digital Transformation Disruptive Technology Enterprise IT Enterprise Acceleration Enterprise Software Next Gen Apps IoT Blockchain CRM ERP CCaaS UCaaS Collaboration Enterprise Service Chief Information Officer Chief Technology Officer Chief Information Security Officer Chief Data Officer Chief Executive Officer

SuperNova Awards Finalists to be Announced August 28, 2014

SuperNova Awards Finalists to be Announced August 28, 2014

This year's SuperNova Award finalists will be announced on August 28, 2014.

SuperNova Awards Logo

We intended to announce the SuperNova Award finalists today, but the volume of applications combined with the fact that we extended the application submission deadline meant that the judges had less time than they would have liked to thoroughly evaluate all applications. We're extending the judging deadline so the judges can give your applications the attention they require for thorough review. 

We're sorry for any inconvenience this has caused. 

Please check back on August 28 when we will announce this year's SuperNova Award finalists!

Data to Decisions Future of Work Marketing Transformation Matrix Commerce New C-Suite Next-Generation Customer Experience Tech Optimization Innovation & Product-led Growth AR Executive Events Chief Customer Officer Chief Digital Officer Chief Executive Officer Chief Financial Officer Chief Information Officer Chief Marketing Officer Chief People Officer Chief Procurement Officer Chief Supply Chain Officer

Who’s on first?

Who’s on first?

1

I spend a lot of time talking about organizations enabling their employees through the use of mobile. It’s truly the only way to ‘win’ at this game. When you enable your users to be more flexible and agile they become more efficient and productive. What more could you ask for? The question always turns to how do you actually enable your people. You start with the FUN principle (Focus on the Users’ Needs) and you build apps that enable them to do what they need to do, when and where they need it. There are many issues with building apps and if you focus on their needs you get most of the way there. Yet, there is still the fundamental issue when building an app that someone can use anywhere and at anytime. How do you know who that somebody is?

whos_on_firstThis is one of the fundamental problems of mobile. You need to know who the person is using the app and you have to make sure it’s them when they are using it. While it sounds simple, it’s not like you can actually be there in person and watch them press the buttons. Hence the practice of identity and access management (IAM) is born.

One of your jobs as the keepers of mobile for your company is to protect their data assets. This used to be somewhat easy. People sat at their desks and were given IDs and Passwords to login to their machines. You knew who was accessing what data at any time since the computers were too heavy to move and so between their ID and password and what computer they were using you were all set. That became harder when laptops were rolled out but you enforced VPNs and gave out RSA tokens to make sure you had a second factor of authentication for your user.

This all went out the window when the iPhone came out. All the sudden you had devices that could go anywhere and at the same time could always be connected. Not only that, but in the beginning they didn’t even have the ability to connect via VPN. That didn’t stop people from wanting to get their email on these devices and then start to do real work on them. Information Security (Infosec) just wasn’t ready for this to happen. It immediately became a no that was overridden by every single person who had one of the devices (another example of shadow innovation). A solution had to be found.

Hence, you now hear the term identity and access management being thrown around. This isn’t a new concept but one that, to be honest, wasn’t ready for the user revolution that mobile brought into the work environment. The first response to mobile enablement was not to allow anything on the device, and the second response was to make people use a VPN to connect to work. It was following the same path of legacy thinking that led to MDM becoming popular. The only issue was that none of these ideas were really good solutions, mostly due the fact that they weren’t implemented well. These solutions didn’t sit well with users because they were using consumer apps and saving their data and keeping stuff confidential and it was easy. They didn’t need to know a different password for each app and enter it every time they opened the app. They just clicked on an app and did what they needed to do.

The question is though, how does Infosec solve this Abbot and Costello problem for most companies. Abbot saying who’s on first and Infosec responding, yeah, who’s on first? The whole point of Infosec is to protect the data and make sure only the right people (identity) are able to get to the right data (access). The problem, which has yet to be addressed in most companies, is how to do this while following the same FUN principle that we used to design app experiences. As any Infosec person will tell you, they want to enable two-factor authentication (independent means of identifying you) on your device and apps and yet they don’t really care about the experience (not all Infosec is this way). In order to get user buy-in, the experience of using work apps has to be transparent and easy, not something that gets in the way. Otherwise users will find another way/app to get their stuff done and that is guaranteed to be insecure.

The two pieces leading the way here are single sign on (SSO) that is integrated across all apps and a second simple form of authentication (2FA) besides your login. SSO means that once you sign into one work app that same credential is used for other work apps you may use in that same session. You no longer have to sign into each one individually as you switch between them. 2FA means that a second way to authenticate you, which may be a certificate on the actual device or biometrics like your fingerprint among others are used to assure you are you. These pieces need to be explained to your app developers and have to be easy for them to setup and use. Only when they are planned well and made simple to integrate into any app will they help to solve the IAM problem that all companies face. In the end, it means that you have to involve your Infosec folks when you are designing your apps to enable your users, not when you are done and want to deploy the apps. Infosec, at the same time, has to adopt design thinking and realize that it’s all about the user experience. When those two things happen, you are well on your way to securely enabling your users while protecting your data.

New C-Suite Digital Safety, Privacy & Cybersecurity Infosec Security Zero Trust Chief Information Officer Chief Information Security Officer Chief Privacy Officer