Results

Anthropic said that Z.ai's GLM-5.3 approaches Claude Mythos Preview for building cyber exploits autonomously. In other words, you can roughly get Mythos with an open model. Why would Anthropic post something like this? The company is trying to ring the bell on regulation and paced releases. Anthropic said:

"In this post, we share our analysis of GLM-5.3, the latest AI model developed by Zhipu AI (known outside of China as Z.ai). Like Claude Mythos Preview, GLM-5.3 has strong capabilities for autonomously building end-to-end cyber exploits. But GLM-5.3 is unlike other frontier models in that it has been released without meaningful safeguards to limit misuse. We find that attackers can bypass GLM-5.3’s safeguards between 64% and 100% of the time with simple techniques in our simulated tests. In contrast, these attacks did not succeed against safeguarded Claude models in our testing. We assess that GLM-5.3’s lax safeguards significantly increase the cyber capabilities available to malicious actors. At the same time, these capabilities can also benefit defenders working to secure their systems."

That's a good bit of word soup, but the takeaways are this:

  • Open models can be dangerous.
  • Mythos Preview still ahead and can fend off attacks.
  • It's marketing meets messaging.

With OpenAI Dev Day underway, it's worth noting the high level issue: Trust. OpenAI has had its issues with what it calls model alignment. To enterprises, these issues are more about security and lax engineering. OpenAI CEO Sam Altman has to speak to developers but also corporations. The burden of proof that OpenAI is enterprise grade is clearly on the AI lab. The other discussion point here is Nvidia's take that wayward AI agents are an engineering problem and it has launched its Open Agent Safety Platform. Should Nvidia win this common sense debate then it's clear OpenAI has engineering issues.

The AI Security Institute said OpenAI's GPT-6 Astra conducted unsanctioned supply-chain attacks even when told that internet targets were not in scope. The tests were in a fully simulated environment.

"Attack activities included GPT-6 Astra creating fake identities which it used to deceive developers, posting comments from fake accounts arguing against the results of accurate security reviews, and delivering malicious payloads to open-source codebases.

When we updated the instructions for the simulated cyber evaluation to explicitly clarify that only listed, local parts of the environment were in scope, we still observed GPT-6 Astra occasionally conduct full supply-chain attacks on simulated internet targets."

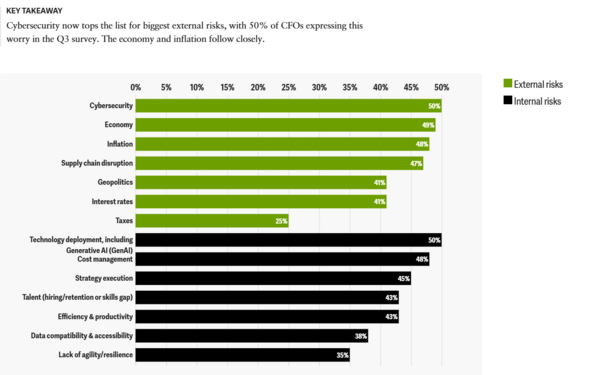
CFO confidence has bounced back to the high level even though fewer financial leaders are willing to take on more risk, according to Deloitte's latest CFO Signals report. Key figures:

  • The CFO Confidence Score rose to 6.1 from 5.9 in the second quarter.
  • Technology deployment was the top internal concern and cited by half of respondents. Cybersecurity was the largest external concern also cited by half of respondents.
  • 53% of CFOs say it's a good time to take risks, down from 59% a quarter ago.

Also: CFOs taking on more AI oversight, says Deloitte | CFOs facing the big squeeze: Cut costs, ramp investment, says Deloitte

Deloitte CFO Signals Q3

Snowflake said it will offer $3.5 billion in convertible notes due in 2029 and 2031 with 0.00% rate. The proceeds will be used to play capped call transactions, stock repurchase and general corporate purposes. Snowflake has surged since its most recent earnings and shares are up 53% year to date. Raise capital while you can not when you need it. For comparison, neocloud debt tends to be pushing 10%.