


AI cybersecurity moving to Elastic's court
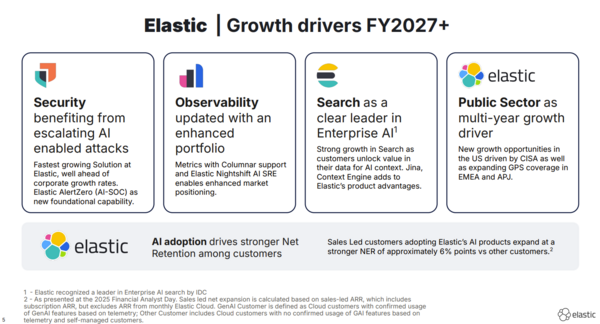
Elastic is gaining momentum in cybersecurity since defending against AI-driven attacks requires a more holistic view of the technology stack including context, observability, telemetry and data.
In October, Elastic launched AlertZero, an agentic layer built into Elastic Security and a team of specialized agents. These agents—Triage Watch, Hunt Watch, Detection Watch and Forensics Watch--take a distinct role in security and responding to threats.
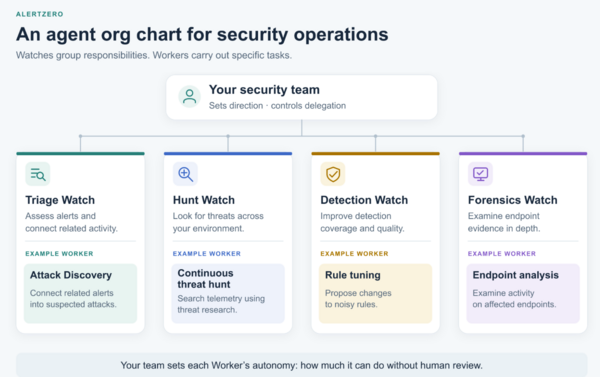
AlertZero is also tightly integrated with Elasticsearch and Elastic Cloud. Elastic's AlertZero is the latest installment of Elastic Security capabilities such as Attack Discovery, ES|QL, Agent Builder and Elastic Workflows.
Elastic's approach with AlertZero appears to be showing early returns. Speaking on the company's second quarter earnings call, Elastic CEO Ashutosh Kulkarni said:
"A leading global investment management company significantly expanded its use of Elastic Security in an 8-figure deal, 3-year renewal that nearly doubled the size of its relationship with Elastic. Serving millions of investors globally, the organization now relies on Elastic as its sole enterprise SIEM to help protect the applications, infrastructure and systems supporting its core financial operations.
Over the past 3 years, its security data volumes have nearly doubled as the customer expanded its use of Elastic endpoint, attack discovery, AI and machine learning and observability for critical security infrastructure. The customer views using AI as essential to keeping pace with increasingly sophisticated AI-driven threats and is now looking to AlertZero and Elastic user and entity behavior analytics to give security analysts faster access to relevant data, automate more of the investigative process and strengthen insider threat detection."
Elastic is planning a webinar on the new AlertZero AI-SOC tool Jan. 7 at 11 am as part of a series on Elastic Security.
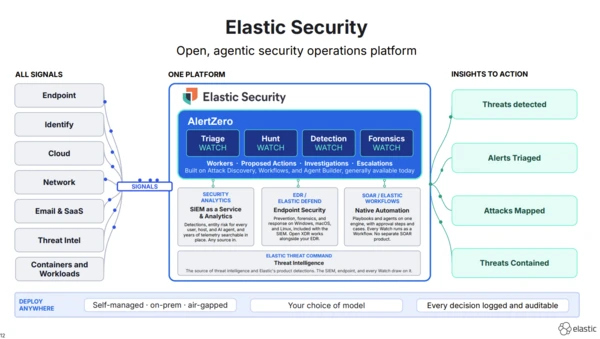
The big picture here is that cybersecurity is broadening out beyond traditional cybersecurity vendors. Kulkarni said data, context, cybersecurity and vulnerability are all blending together and starting to overlap. "What you're seeing now in the market is a desire to look at full-signal or full-stack observability," said Kulkarni, referring to the need to track AI agents.
"With AlertZero, every human SOC analyst can have their own team of silicon agents, helping them defend against even the fastest and most complex cyberattacks. Unlike agentic SOC tools that layer AI on top of a disconnected tool set, AlertZero brings agentic automation directly into Elastic Security. That gives it cross-domain context, relevance-driven evidence gathering and unified workflows for triage, investigation and response," said Kulkarni.
Elastic also recently announced Elastic nightshift AI SRE, which continually detects and investigates issues and tests multiple root-cause hypotheses for causes. Elastic is addressing the reality that cloud-native systems produce more telemetry than humans can review and agentic development has made the problem worse.
The nightshift launch is well timed given the recent run on outages. Kulkarni said cybersecurity issues and outages appear to be linked.
"There are really two factors at play here. So the first is that because of frameworks like ARTEX, the ability to use both proprietary as well as open LLMs to launch AI-generated attacks, there's a tremendous amount of increase in both vulnerability discovery and weaponization. And that is creating a tremendous amount of risk and concern for every CISO, for every organization out there," he explained. "The second thing that we are seeing is as organizations are rushing to patch their software, their systems, given the discovery of these vulnerabilities, it's putting them in a position they've never been in. Both of these factors are creating a lot of difficulty. And the most important thing that they care about right now is prioritizing security. We are seeing a definite increase in the number of conversations that we are having on security.
Elastic's integrated approach to security, search, context and observability is paying dividends. Elastic ended the second quarter with more than 1,830 customers spending $100,000 or more in annual contract value. For good measure, Elastic said it has acquired HoneyHive, which will expand its agent observability and evaluation capabilities.
Kulkarni's bet is that Elastic's reach across systems and data stores will yield dividends.
"When you're dealing with the security problem, it becomes really complex to be able to bring in all of that data, normalize it, really understand what the correlations are and find patterns across all of that data. That is something that very few security vendors are able to do at scale. So when it comes to these large kinds of government agencies, these large kinds of banks, insurance organizations and so on, we just have a wonderful advantage," Kulkarni said. "We can do that both in the cloud and self-managed in their own data centers. So it is something that we lean in on."
More on Elastic:
- Elastic's bets on context pay off as AI agents need to be more accurate, cost effective
- Constellation ShortList™ Autonomous IT Platforms
- ShortList Spotlight: Elastic’s Data-First Approach to Autonomous IT
- Elastic Security bets on native Workflows, data-centric approach
- Elastic sees early traction with Agent Builder, context play, hybrid architecture
Larry Dignan is Editor in Chief of Constellation Insights at Constellation Research, where he leads editorial coverage focused on enterprise technology, digital transformation, and emerging trends shaping the future of business. He oversees research-driven news, analysis, interviews, and event coverage designed to help technology buyers and vendors navigate complex markets with clarity and context. ...
Read morePublished
Author
